

Novee adds external attack surface testing to platform
Mon, 16th Nov 2026 (Today)
Novee has added external surface testing to its AI penetration testing platform, extending the product from application testing to internet-facing assets.
The feature is designed to help security teams identify unknown external assets, test whether newly disclosed vulnerabilities affect them, and determine whether those weaknesses are exploitable. The system can start with only a domain name and build a prioritised list of validated issues.
It brings external attack surface testing into the same platform Novee uses for web, mobile and AI application pentesting. Teams can move from broad external discovery to deeper application testing without changing tools, while keeping findings in a single issue list.
External attack surface management products have become more common as companies try to track internet-facing systems such as subdomains, staging servers and public IP addresses. Novee is positioning its latest release as a way to go beyond asset discovery and severity scoring by testing whether reported exposures can actually be exploited.
The system can also test findings imported from third-party external attack surface management tools against live assets. It explores the external environment, builds context across assets and services, and looks for vulnerabilities and attack paths that may not appear in separate scans.
Single workflow
Novee says the combined set-up is intended to reduce the need for separate products for external discovery and application pentesting. If a discovered host needs further analysis, teams can promote it into a grey-box or white-box application pentest, with discovery context and findings carried across.
That unified approach reflects a wider trend in cyber security towards linking exposure management more closely with testing and validation. Security teams often face long lists of flagged assets and vulnerabilities from scanning tools, but still need to work out which ones present practical risk.
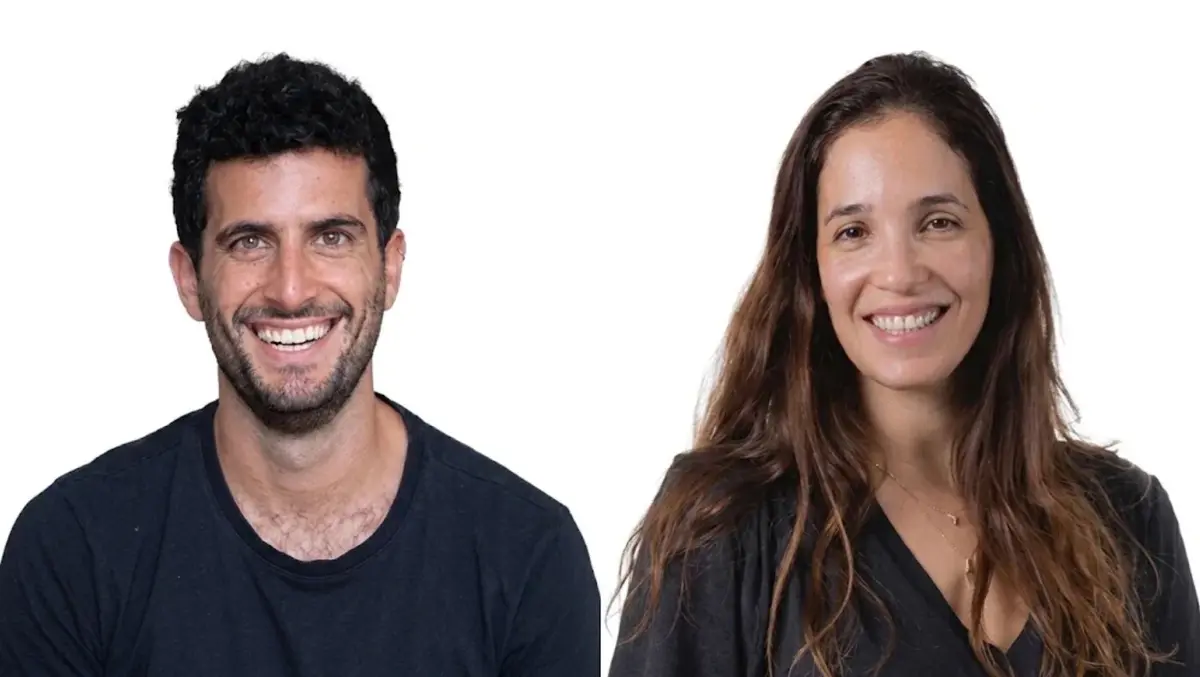
Netta Rager Dan, Vice President of Product at Novee, said the product was built to help teams respond more quickly when major software flaws are disclosed.
"When a critical new CVE is disclosed, security teams need answers fast - which assets are affected, what's actually exploitable, and where to focus first," said Netta Rager Dan, Vice President of Product at Novee.
"Traditional EASM tools show you what's exposed, but don't give you the full picture of real risk. Novee brings external discovery and offensive testing together, so teams can validate emerging threats, uncover vulnerabilities attackers could exploit, and go deeper into applications - all in one platform," Dan said.
Testing controls
The feature is built for controlled testing from outside a customer's perimeter. Teams approve the testing scope before work begins, and the process does not require agents, software installation or customer-provided credentials.
Novee says exploits are validated without destructive payloads and that traffic remains within configured limits. This is intended to reduce the risk of service disruption, load spikes or unnecessary alerts for security operations teams.
The launch adds to a period of rapid development at the company, which describes itself as an AI penetration testing provider. Novee says it was founded by Ido Geffen, Gon Chalamish and Omer Ninburg, and has raised USD $51.5 million within four months of inception from investors including YL Ventures, Canaan Partners and Zeev Ventures.
Amit Zeevi, Product Manager at Novee Security, outlined the rationale for expanding testing beyond known applications into the wider internet-facing environment.
"Attackers don't limit themselves to the applications you're already testing. They look for anything exposed to the internet - forgotten subdomains, staging servers left online, and infrastructure your team may not even know exists. When a critical new CVE emerges, they look for ways to exploit it, often chaining multiple weaknesses into a larger attack," said Zeevi.