
Report flags short-term ties in US research security
Mon, 26th Oct 2026 (Today)
Digital Science has published a report on research security in U.S. federally funded science. It found that 48.2% of researchers linked to both a restricted entity and a U.S. institution held the U.S. affiliation for 24 months or less.
The report examined federally funded research from 2016 to 2025 and identified 14,549 researchers with short-term affiliations over that period. It assessed more than 3 million publications acknowledging U.S. federal support and covered about 1.9 million researchers with U.S. affiliations.
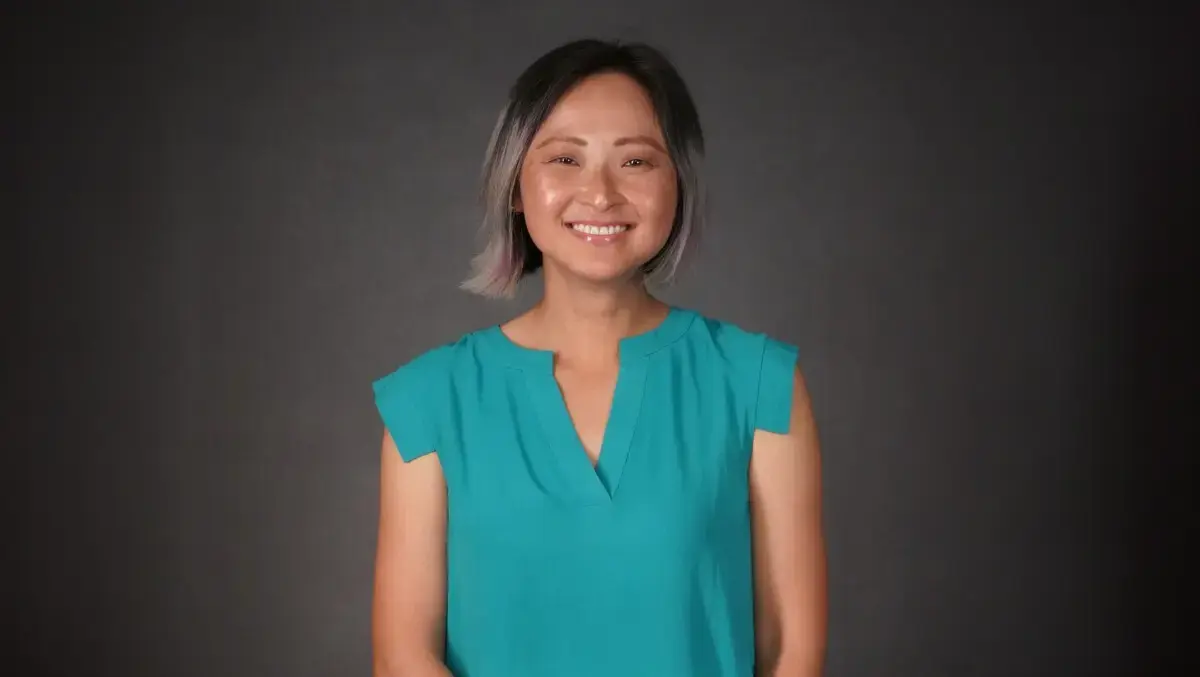
Authored by Dr Xueying Han, Head of Research Analytics at Digital Science, the study used publication, funding and researcher affiliation data from the company's Dimensions database. It cross-referenced affiliations against restricted-entity lists maintained by U.S. and allied government agencies.
The findings focus on visiting scholars and other short-term researchers whose previous institutional ties may not be captured by current disclosure processes. During a U.S. appointment, a researcher's affiliation of record is typically the host institution, which can leave earlier links outside existing checks.
The study is presented as the first ecosystem-wide assessment of research security exposure across U.S. federally funded research. It comes as federal policy tightens, with new funding prohibitions and restricted-party collaboration requirements due to take effect in 2026 and 2027.
Short-term ties
Digital Science said the broader level of exposure identified in the data was modest and falling. The share of federally supported publications carrying a restricted-entity affiliation fell 30% from 2018 to 2025, while 2% of researchers held both a U.S. and restricted-entity affiliation in the same year.
The report does not argue for broader limits on international collaboration. Instead, it proposes a narrower model of oversight based on research sensitivity and an institution's tolerance for risk.
Its recommendations include assessing research sensitivity, screening all researchers consistently, actively monitoring for security risks or exposure, and applying cooling-off periods where institutions judge them necessary.
"There's a tendency to treat openness and security as opposites, but our data suggest that isn't quite right. Addressing this oversight issue doesn't require restricting collaboration. It requires institutions and agencies to know where to look and to act appropriately," said Dr Xueying Han, Head of Research Analytics at Digital Science.
Policy gaps
Beyond short-term appointments, the analysis also identified what it described as structural weaknesses in current federal policy. These included the lack of a unified list of critical technology areas, inconsistent thresholds for collaboration, and mandates that apply the same level of scrutiny across different types of research.
The report argues that those issues can make it harder for institutions and agencies to direct checks towards the areas of greatest concern. Its central point is that scrutiny should be matched more closely to the level of risk, rather than applied evenly across all international research links.
Digital Science's analysis comes amid increased attention to research security in the United States, particularly in federally backed work and collaboration with entities on government restriction lists. Universities and research organisations have faced growing pressure to strengthen disclosure systems and due diligence as compliance requirements expand.
The report presents short-term affiliations as a blind spot in that framework because they may not fit neatly within disclosure rules focused more on current institutional relationships. That means a visiting scholar's earlier association with a restricted entity may not be visible through normal administrative records at the host institution.
Han said the findings are intended to help research security officers, university leaders and federal programme managers. "This assessment gives them data they can use to better understand where risks are concentrated and focus attention where it is most warranted. That can strengthen research security without treating every international collaboration as equally risky."