

Governance tops CISO concerns in hybrid AI adoption
Tue, 29th Sep 2026 (Today)
Gigamon has published research showing that governance has become a leading concern for chief information security officers as companies adopt hybrid artificial intelligence. The survey covered more than 300 CISOs globally.
The findings suggest many security leaders are struggling to keep pace as businesses deploy a mix of public, open-weight, specialist and privately hosted AI models across their operations. This creates more connections between applications, infrastructure and corporate data, making oversight harder.
Governance featured prominently in the responses. Some 43% of CISOs ranked corporate AI governance as a top security priority, while 80% said inadequate governance around unsanctioned AI use was the main challenge in securing data.
AI-linked security incidents also featured heavily in the research. Among organisations that suffered a breach in the past year, 83% reported AI-related security incidents, including internal leaks into AI systems and unsanctioned AI use, each cited by 30% of respondents.
Board oversight emerged as another pressure point. Seven in 10 CISOs said a lack of understanding of security best practice at board level could cause AI adoption to outpace security readiness, and 41% ranked better board understanding of AI risks and benefits among their main priorities for the next year.
The research also pointed to personal pressure on security leaders. More than one in four CISOs said they were concerned about losing their job after a serious cyber incident.
Visibility gaps
A lack of visibility into AI-related activity was one of the clearest themes in the study. Some 76% of CISOs said limited visibility into AI-driven traffic was a major barrier to securing AI adoption, while 45% said they were prioritising better visibility into AI-driven data flows across hybrid cloud infrastructure.
That concern persists despite continued spending on security tools. Nearly nine in 10 CISOs said their organisations had deployed new tools to improve detection and visibility, yet breaches rose 18% year on year.
The survey highlighted a sharp difference between security leaders and other senior executives on incident response. Only 27% of CISOs said their organisation could identify the root cause and restore normal operations within 72 hours after an incident, compared with 48% of other C-level executives.
Lateral, or east-west, traffic inside networks was identified by 36% of CISOs as the area of greatest breach risk. Encrypted traffic was another focus, with 86% saying visibility into it was critical for post-quantum computing readiness and 89% saying better visibility could help reduce cyber insurance premiums.
Australian response
The Australian results showed local CISOs placing greater emphasis on AI-specific safeguards than their global peers. In Australia, 56% said they were prioritising AI and large language model security guardrails and monitoring controls, compared with 41% globally.
Australian respondents also reported a stronger focus on detection and response tied to AI threats. Some 54% said they were prioritising stronger detection and response for AI-related threats, versus 40% of CISOs worldwide.
These figures suggest Australian organisations are moving earlier on some aspects of AI risk management, even as the broader governance and visibility issues seen in the global sample remain unresolved.
CISO mandate
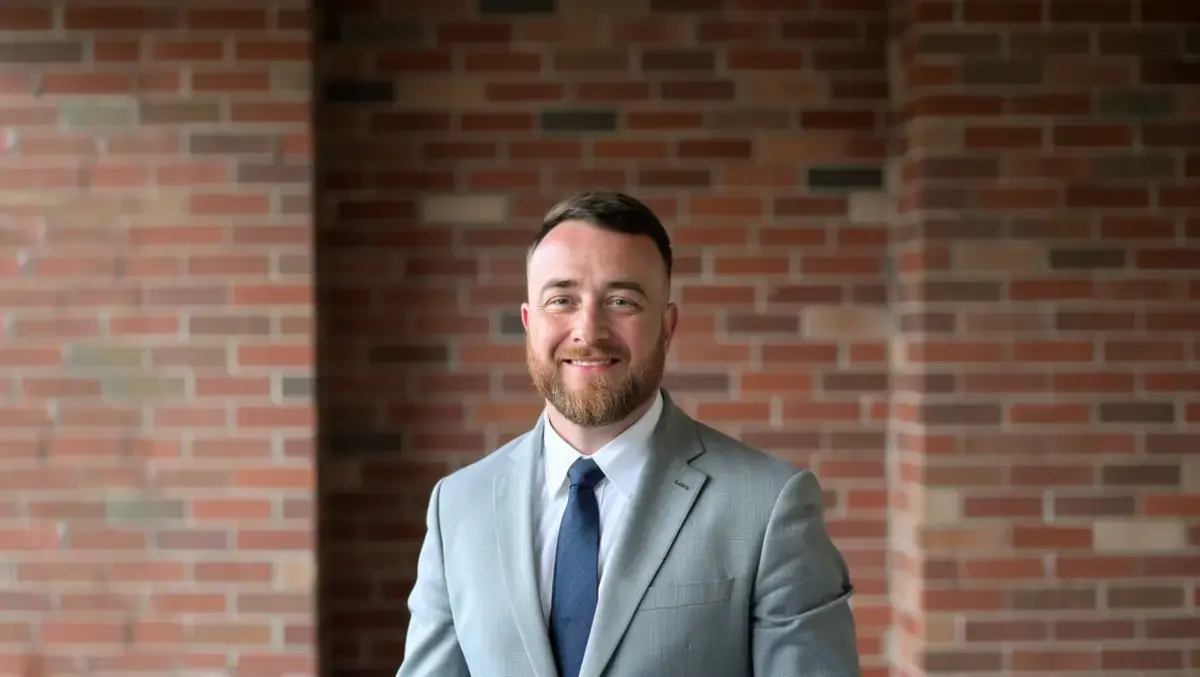
Grant Yacomeni, CISO at Gigamon, said the core challenge was understanding where AI is being used and how it connects with other systems.
"Hybrid AI is moving faster than governance," Yacomeni said.
"Organisations want the flexibility to choose the right AI model for every workload, but that flexibility depends on having the visibility to govern it. CISOs need to understand which AI systems are in use, how they interact with applications and data, and what is happening across those connections. You cannot govern what you cannot see."
Gigamon found that 87% of CISOs viewed deep observability as foundational to securing AI deployments. In practical terms, that means drawing more information from network traffic, including packets, flows and application-aware metadata, to help security teams understand how systems and data interact across hybrid environments.
The broader study, now in its fourth year, surveyed more than 1,000 security and IT leaders across Australia, France, Germany, Singapore, the United Kingdom and the United States, including 307 CISOs. Of those surveyed, only 27% of CISOs said their organisation could identify the root cause and restore normal operations within 72 hours after an incident.